
Initia’s $2.7 Million Rollup Heist: The Hidden Crisis Shaking Blockchain Security to Its Core—What They Don’t Want You to Know!
Ever wonder what happens when someone finds a clever little crack in the blockchain armor and decides to exploit it? On October 23rd, Initia—a Layer 1 blockchain coupled with a modular roll-up network—experienced a seismic security breach that turned heads and wallets upside down. Imagine minting 2 million tokens out of thin air with a single transaction—and then swiftly turning those tokens into real Ethereum and USDC, exploiting cross-chain bridges like a pro hacker on caffeine. This wasn’t just any exploit; it was a high-speed heist that pushed the boundaries of blockchain security and echoed last September’s Liquid Network debacle. Despite the chaos, Initia’s native token, INIT, surprisingly climbed by nearly 12%, proving once again how unpredictable the crypto world can be. In a year already riddled with skyrocketing security incidents, this episode raises a pressing question: How safe is our digital money really, when vulnerabilities can be weaponized so fast? Buckle up, because this story dives deep into the guts of a hack that’s shaking the foundations of cross-chain trust. LEARN MORE.
Initia, a Layer 1 blockchain and interwoven modular roll-up network, suffered a major security incident on 23rd October. An attacker allegedly exploited a vulnerability in its blockchain to create tokens without permission and withdraw real assets from cross-chain bridges.
According to the investigation, the attack began at 14:59:26 UTC when the exploiter used a single signed transaction to mint 2 million AUSD tokens out of thin air on Initia.
The transaction reportedly consumed 135,888 gas and called a ‘Move’ function directly, without requiring a cross-chain bridge message. So, instead of breaking the bridge’s security verification process directly, the attacker hacked a vulnerability in the token-minting mechanism.
All about Initia’s security incident
The attacker didn’t stop there though. Instead, they exploited cross-chain infrastructure to convert these unauthorized tokens into real assets on Ethereum [ETH]. So, roughly 153 seconds after the initial mint, a valid LayerZero message enabled the release of 1.4 million AUSD from the Ethereum-side adapter.
At the same time, the attacker also withdrew 105 ETH from the native-ETH adapter and obtained 1.08 million USDC through Circle’s Cross-Chain Transfer Protocol (CCTP). According to researchers, the attacker converted the funds into Ethereum through decentralized trading services, including 1inch and 0x.
Here, within approximately 7 minutes of the initial mint, around $2.65 million had reached Ethereum. The consolidated funds later amounted to 1,135.52 ETH, worth approximately $2.73 million, held in a newly created wallet.
This seemed to be very similar to September’s Liquid Network incident, where a software bug enabled the creation of unauthorized L-BTC and the withdrawal of real Bitcoin.
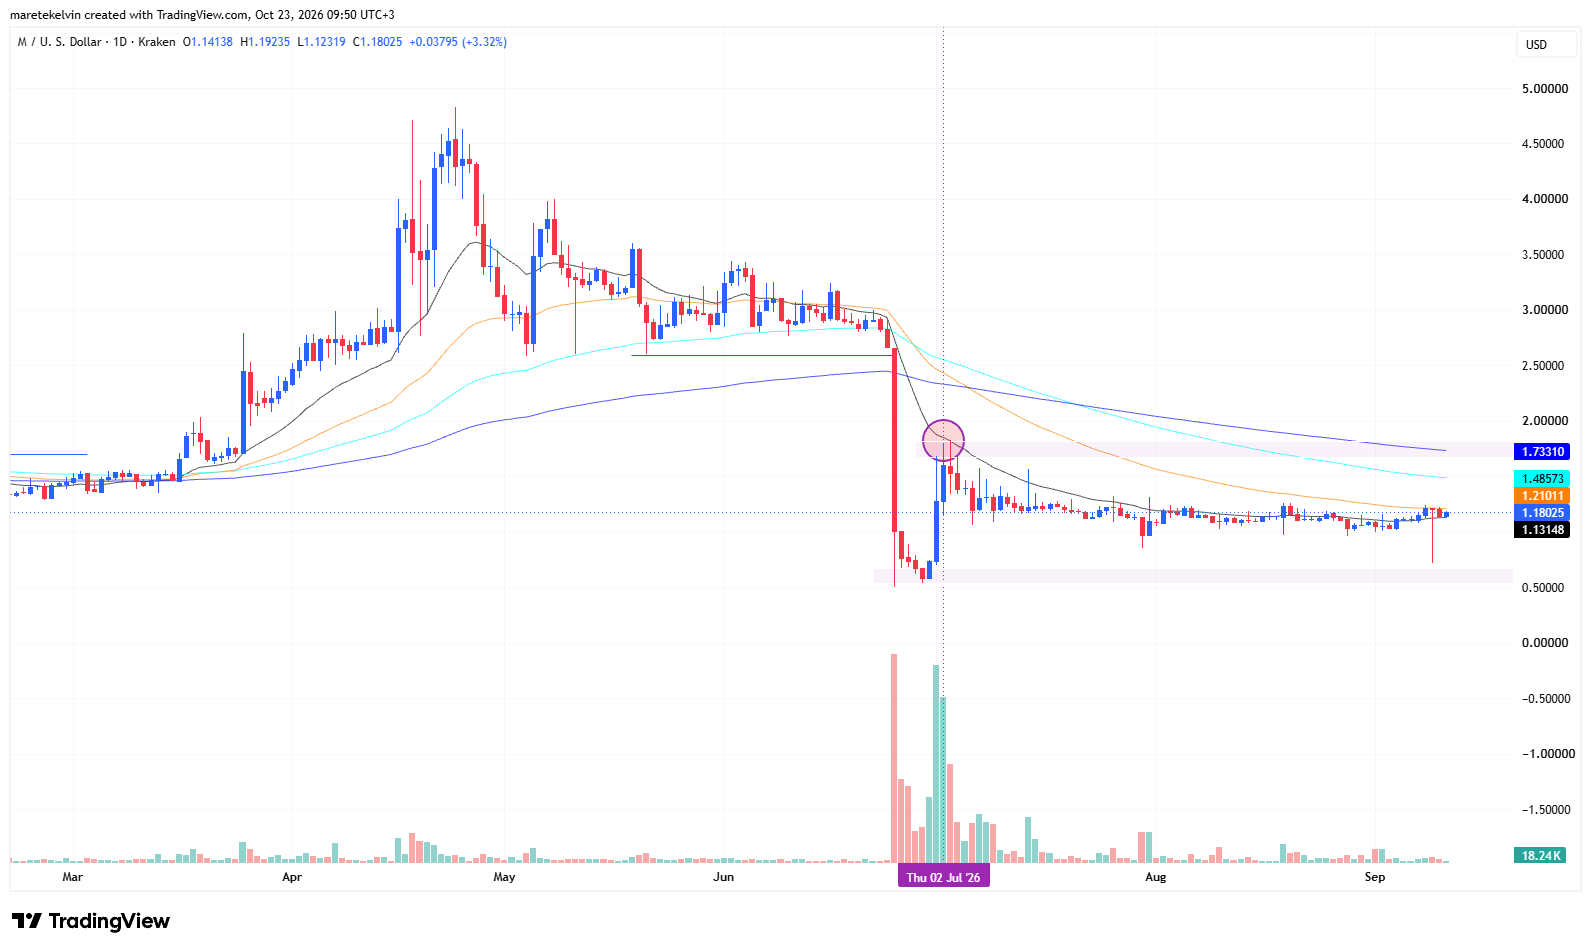
As expected, the incident forced Initia to halt its L1 blockchain and roll-ups. And yet, despite this rollercoaster, Initia’s token INIT was trading at $0.1484 at press time after a hike of 11.7% in the last 24 hours.
2026 has so far being a tricky year for security incidents like these. In fact, AMBCrypto’s recent report found that crypto security losses surged by 55% to $1.18 billion in Q3 2026, while reported incidents jumped from 67 to 107.
Final Summary
- Transaction reportedly consumed 135,888 gas and called a ‘Move’ function directly, without requiring a cross-chain bridge message.
- This was very similar to September’s Liquid Network incident, where a software bug enabled the creation of unauthorized L-BTC and the withdrawal of real Bitcoin.
Dog Dental Wipes for Teeth Cleaning, Finger Toothbrush Wipes for Dogs Cats,Dog Teeth Cleaning Wipes Reduce Bad Breath & Plaque Tartar, No-Rinse Daily Oral Care,Dog Toothbrush & Toothpaste Alternatives
$22.99 (as of October 24, 2026 03:23 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
ARM & HAMMER Slide Platinum Easy Clean-Up Clumping Cat Litter, 18 lbs | 24/7 Odor Control, Triple-Action Freshness, Non-Stick, Low Tracking, 99.9% Dust Free, Multi-Cat Formula, Scented
$17.99 (as of October 24, 2026 03:13 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Camvivid Stainless Steel Litter Box, Covered with Lid, 17.3x13.4x7.9in, Litter Scoop & Anti-Skid Stickers, High Walls, Odor Free, Non-Stick, Low Entry, Easy Clean for Kitten Multi-Cat Indoor Home
$25.99 (as of October 24, 2026 03:23 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Bloom Nutrition Zero Sugar Energy Drink, Apple Crisp, 12oz 12pk | 180mg natural caffeine with prebiotics, green tea extract & lychee for energy, focus and feel-good refreshment.
$24.99 (as of October 24, 2026 03:13 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)

Post Comment